Lighter halts withdrawals after leaked API key drains $10.4 million
Author: Crypffalo Research · 23:56 16/11/2026
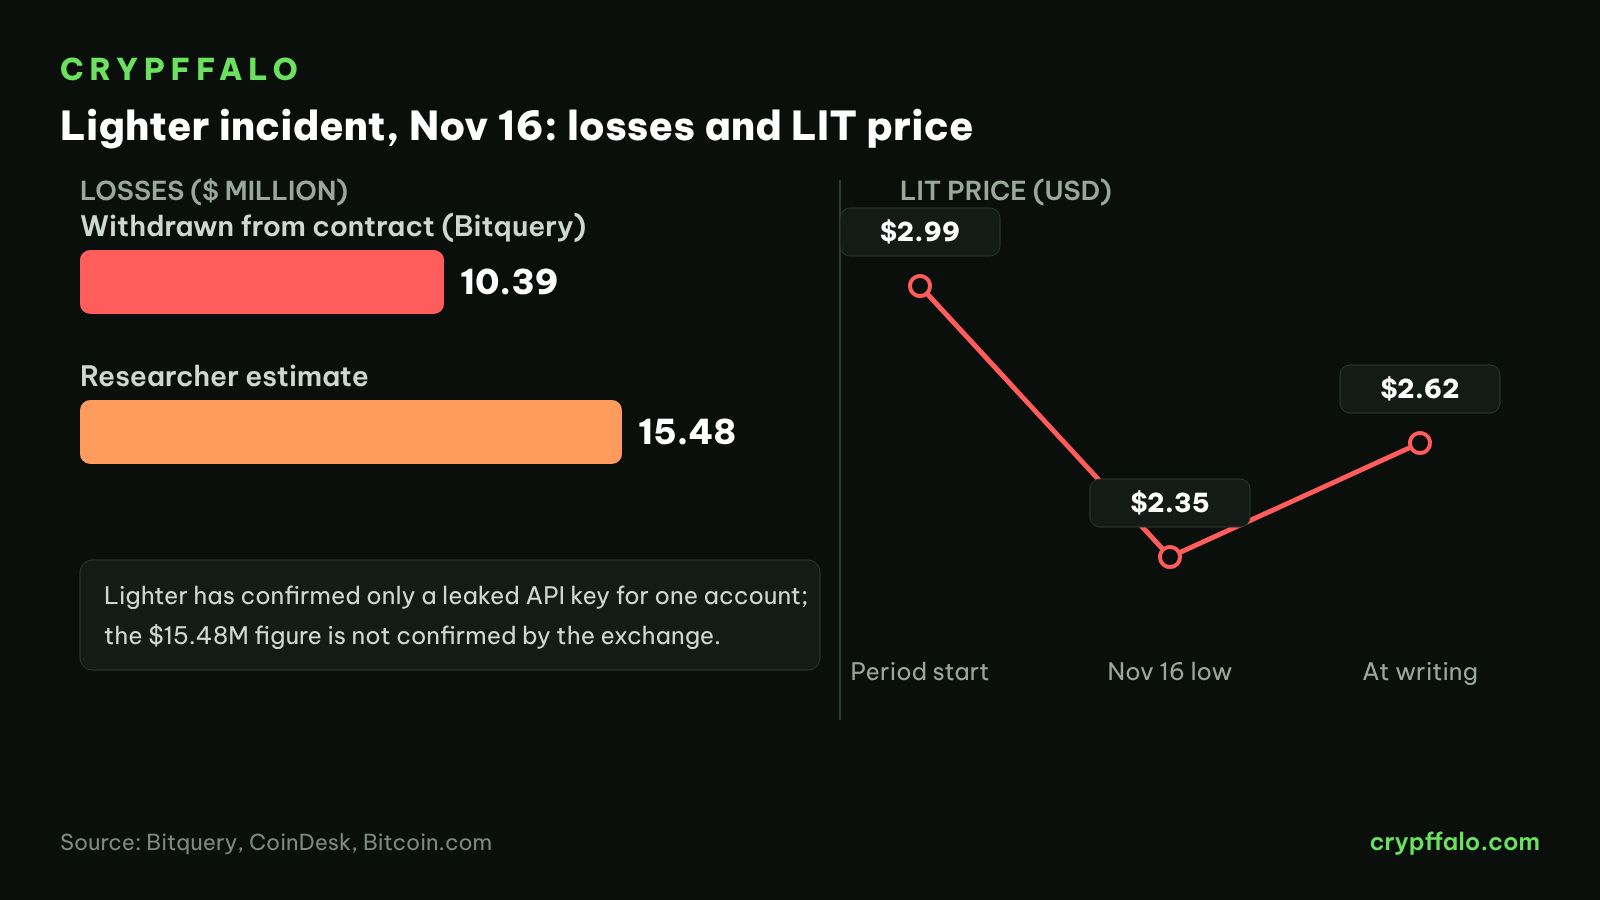
Decentralized perps exchange Lighter paused withdrawals after an attacker used a leaked API key to pull about $10.39 million in USDC; Lighter says its contracts were unaffected, while LIT fell about 17–20% at one point.

Decentralized perpetuals exchange Lighter halted all withdrawals on Nov 16 after an attacker pulled roughly $10.39 million in USDC from the platform's Ethereum contract. On-chain data from Bitquery shows the funds leaving at around 10:11 UTC.
Lighter said the incident stemmed from a leaked API key belonging to a single external trading account, not a flaw in its smart contracts. The project's LIT token fell roughly 17–20% at one point during the day before recovering part of the move.
Key takeaways
- Confirmed on-chain loss: about $10.39 million in USDC withdrawn, per Bitquery and Bubblemaps; some researchers put potential losses near $15.5 million, a figure Lighter has not confirmed.
- Cause: a compromised API key for one account; Lighter says the protocol and contracts were not affected.
- Response: withdrawals and new liquidity pool creation paused, "Guardian mode" switched on, and the security council preparing a contract upgrade.
- Attacker flows: most of the USDC was swapped to ETH via CoW Swap, with part of it sent to Hyperliquid to buy a Monero-linked token.
- LIT token: slid from around $2.99 to a low of $2.35, then traded near $2.62–$2.70.
How the funds were drained
According to an analysis by researcher 0xTria, cited by CoinDesk and crypto.news, the attacker used API access to close the victim's positions and convert holdings into USDC. A public liquidity pool with a 0% fee was then created, and the attacker deposited around $10,000 to own almost all of its shares.
USDC from the compromised account was pushed into the pool in batches of roughly $1 million before the attacker redeemed the shares. The route sidestepped the usual limits on API keys, which cannot send funds directly to unrelated users.
Key moments on Nov 16 (UTC):
- Around 09:40: the attacker's wallet received about $10,000 through a relay, roughly 30 minutes before the withdrawal.
- Around 10:11: 10,393,057 USDC left Lighter's Ethereum contract, according to Bitquery.
- Minutes later: most of the USDC was swapped for ETH through CoW Swap.
- Later on Nov 16: Lighter paused withdrawals, attributed the incident to a leaked API key and set a goal of restoring withdrawals by the end of Monday.
What Lighter has said, and what remains unclear
In its first statement, Lighter said it was investigating a security incident that appeared to involve a single compromised external party. A follow-up update was more specific: one account's API key had leaked, while the protocol and smart contracts were untouched.
The exchange enabled "Guardian mode" on its contract, with its security council set to carry out an upgrade. Lighter also published the attacker-linked wallet address and said it had observed a further withdrawal attempt.
Several points are still pending confirmation:
- Total losses: the $15.5 million estimate comes from researchers tracking two market-maker accounts; Lighter has not confirmed a second successful withdrawal.
- Account owner: some Chinese-language outlets named Abraxas Capital, but major outlets have not confirmed this.
- Compensation: Lighter has not said whether the affected account will be reimbursed, only that recovering funds is its top priority.
- Withdrawals: at the time of writing there was no confirmation that withdrawals had resumed.
South Korean exchanges Upbit and Bithumb also temporarily suspended LIT deposits and withdrawals while the incident was handled, crypto.news reported.
Crypffalo data view
Crypffalo's DeepDom data for the 24 hours to 23:00 GMT+7 on Nov 16 shows LIT under far heavier selling pressure than the broader market:
- Price: LIT at $2.63, down 8.84% over 24 hours; BTC at $64,441, down 0.43% → the drop was concentrated in LIT and did not spill into Bitcoin.
- Liquidations: $0.89 million of LIT longs liquidated versus $0.37 million of shorts → longs took the bigger hit.
- Aggressive flows: LIT futures net -$5.8 million and spot net -$0.69 million → sellers dominated both markets.
- Order book ±1%: about $0.22 million of LIT bids versus $0.17 million of asks → the book currently leans slightly toward buyers.
The data matches what news reports describe: LIT was sold hard right after the incident, while BTC was close to flat. See also real-time liquidations.
What it means for crypto markets
At roughly $10–15 million, the incident is far smaller than the major hacks seen in recent weeks and has not put visible pressure on BTC or ETH. The impact is mostly on LIT and on confidence in decentralized derivatives venues competing with Hyperliquid.
- Bull case: Lighter reopens withdrawals on schedule, confirms the problem was limited to one account and lays out a clear remediation plan, helping LIT stabilize.
- Risk case: actual losses prove larger than reported, the reopening is delayed, or more affected accounts surface, pushing users to pull funds.
The episode is also a reminder of API key risk: many funds and market makers trade through APIs, and a single leaked key can be enough to drain an account if an exchange's internal transfer logic leaves a gap.
What to watch next
- Lighter's announcement on reopening withdrawals and details of the contract upgrade.
- Official confirmation of total losses and of the affected account.
- The attacker's ETH on Hyperliquid and any chance of a freeze.
- LIT price action and deposit/withdrawal status on Upbit and Bithumb.
- This week's macro events on the economic calendar.
Frequently Asked Questions
Were Lighter's smart contracts hacked?
According to Lighter, no. The exchange said a leaked API key for one account caused the incident and that the protocol and contracts were not affected.
Did Lighter users lose money?
Reported losses sit with the account whose API key leaked. Even so, all users are temporarily unable to withdraw until the exchange reopens withdrawals.
Why are there two figures, $10.4 million and $15.5 million?
$10.39 million is the amount traced leaving the contract. The $15.5 million figure is a researcher estimate across two accounts that Lighter has not confirmed.
*This content is for information only and is not financial advice.*
Tags: Lighter, Hack, DeFi, LIT, Security
Related articles
- Sky's USDS sees $1.5B USDC exodus after North Korea-linked flows report
- Bitcoin tests $64,000 then slips as Anthropic opens 34% above its record IPO price
- Nvidia beats with $115.8B revenue, but Bitcoin barely moves near $64,500
- Solana Foundation takes majority stake in CoinGecko, eyes onchain trading
- Optimizely attack plants crypto address-swapping malware on 178 sites, including Ledger
- Peraire-Bueno brothers acquitted in $25M Ethereum MEV exploit case